 📊
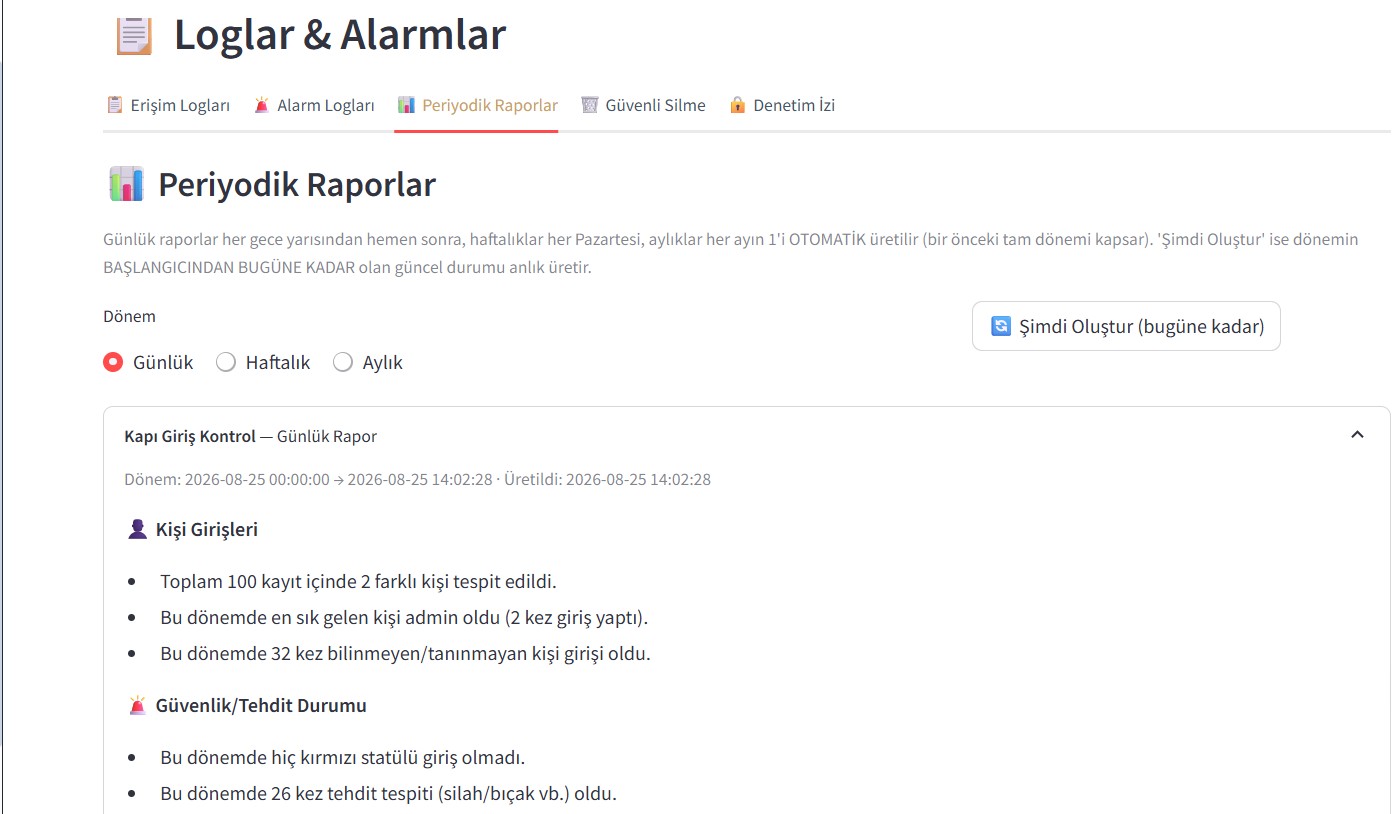
How should camera footage be stored under KVKK?
A practical look at retention periods, access authorisation and audit trail design in a system that runs on a local network.
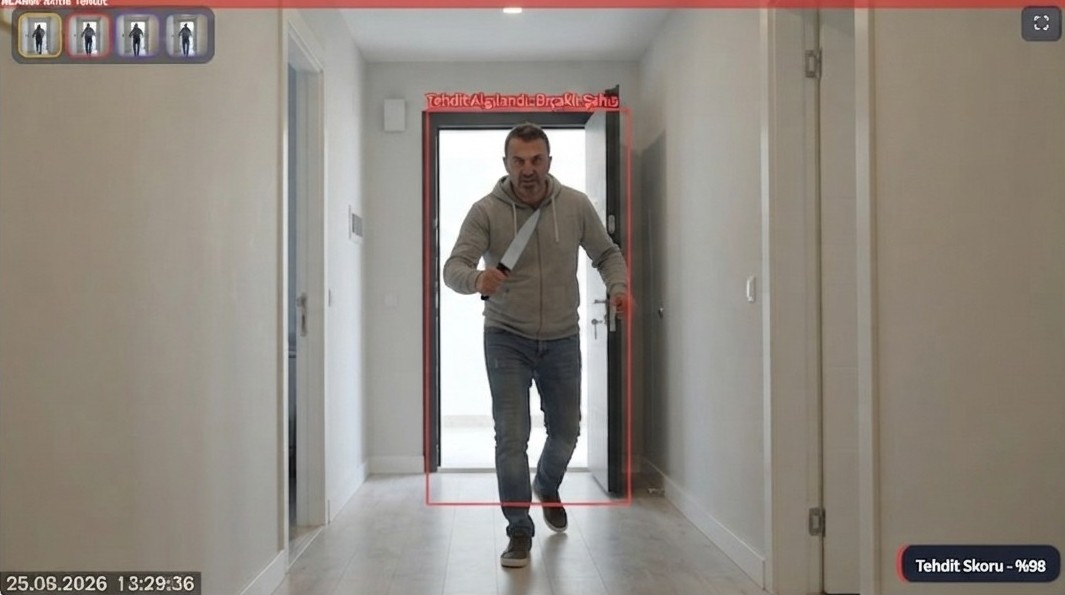 🔪
Local GPU instead of the cloud: bringing latency down to milliseconds
We explain how local processing removes the latency risk that a cloud API call brings to threat detection.
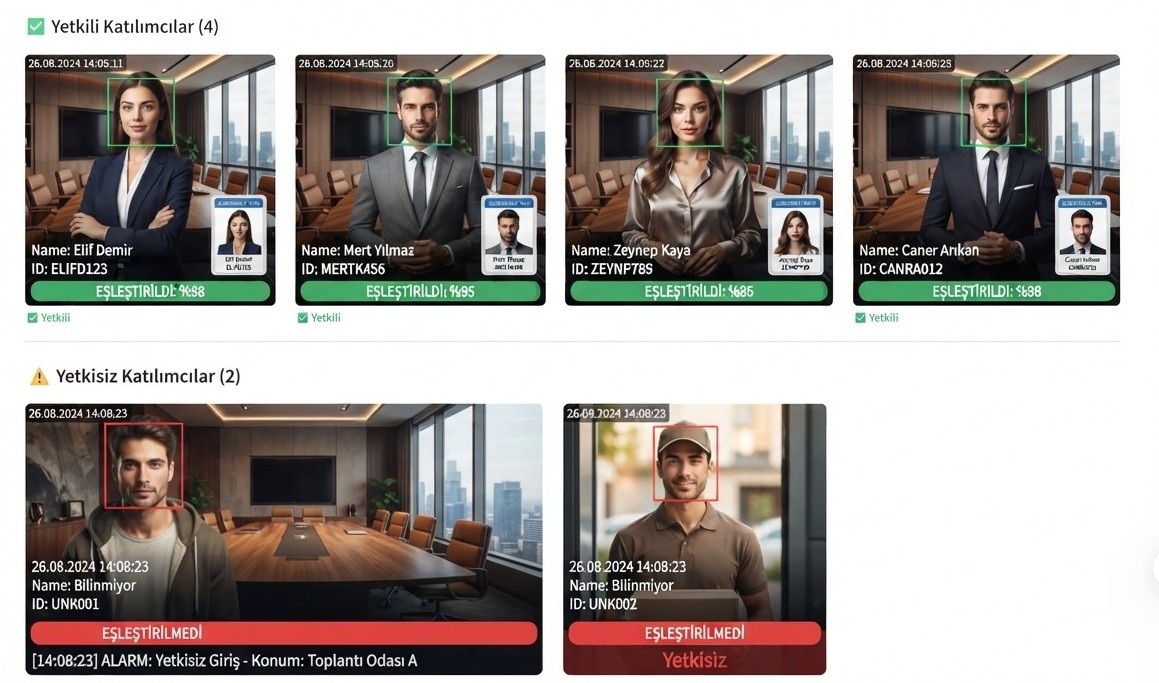 🏢
Moving from manual roll call to automatic attendance tracking
A field note on how Meeting Mode is used in corporate settings in place of sign-in sheets and QR codes.